AI agent governance is the set of controls that keeps every action an AI agent takes inside the authority a person delegated, on every path the agent uses: calls to models, calls to tools over the Model Context Protocol (MCP), and calls to other agents over the Agent2Agent (A2A) protocol. It answers four questions for each action: which agent acted, whose authority it used, which policy applied, and who decided anything high-risk. The answers have to exist before the action runs and stay in a record afterward.
A chatbot that drafts text has a narrow reach. An agent that can read email, query a CRM, run database queries and send messages has the access footprint of a privileged employee, and it chooses its own next step.
This guide covers the three paths agents use, the attack surface MCP and A2A open, the chain problem, a six-control framework and what regulation asks.
Regulatory references verified as of November 20, 2026.
What AI agent governance covers
An agentic AI system plans and takes actions on a person's behalf. Governance for it reviews each action the agent takes. It asks whether this call, with these arguments, at this moment, sits inside the authority a person delegated.
An agent reaches the enterprise along three paths:
- Model calls. Prompts and responses to frontier models in a provider's cloud and to models the enterprise runs itself.
- Tool calls. Database queries, API calls, file operations and messages, often over MCP.
- Agent-to-agent calls. Tasks handed from one agent to another, often over A2A.
Controls on one path leave the other two open. A policy that reads prompts sees nothing of a payment an agent submits through a tool, and a tool allowlist sees nothing of a task passed to a second agent with different tools.
MCP and A2A: the two protocols agents use
MCP connects agents to tools
The Model Context Protocol defines tools as "Functions for the AI model to execute." Its specification, version 2026-07-28, sets out security principles: users must consent to data access and operations, and "Hosts must obtain explicit user consent before invoking any tool." It also states: "MCP itself cannot enforce these security principles at the protocol level." Consent, access control and authorization fall to whoever runs the agents. The MCP security guide covers the tool path in depth, and the glossary covers tool poisoning.
A2A connects agents to other agents
Google announced the Agent2Agent protocol on April 9, 2025. The Linux Foundation launched it as a project on June 23, 2025, and on August 17, 2026, A2A joined the Agentic AI Foundation, which the Linux Foundation hosts, as a hosted project alongside MCP. The specification's latest released version is 1.0.0.
Three parts of A2A matter for governance:
- The Agent Card. "A JSON metadata document published by an A2A Server" that describes the agent's identity, capabilities, skills, endpoint and authentication requirements.
- The Task. "The fundamental unit of work managed by A2A, identified by a unique ID," stateful, with a defined lifecycle.
- Opacity by design. Agents "collaborate based on declared capabilities and exchanged information" and need not share their internal plans or tool implementations. The calling agent sees the result, without the tools behind it.
The specification requires servers to "reject requests with invalid or missing authentication credentials." Whether the person behind the first agent in the chain may ask for this task is a question the protocol leaves to the enterprise.
Where the attack surface opens
The OWASP GenAI Security Project published its Top 10 for Agentic Applications on December 9, 2025. Among the threats it highlights are agent behavior hijacking, tool misuse and exploitation, and identity and privilege abuse. Prompt injection through an email, a document or a tool's output can redirect an agent that has live credentials.
The joint guidance from six national cyber agencies, Careful Adoption of Agentic AI Services, published on April 30, 2026, sorts agent risk into five categories: privilege, design and configuration, behavior, structural and accountability risks.
A public case shows how an instruction inside the model fails as a control. In July 2025, Fortune reported that a Replit AI coding agent had deleted a live company database during a code freeze, wiping data on more than 1,200 executives, after, by the user's account, being told not to proceed without human approval. Replit's chief executive, Amjad Masad, called it "Unacceptable and should never be possible." The instruction sat in the agent's input. A control outside the model applies the same rule whatever the model concludes.
The chain problem in agent-to-agent work
Agent A hands a task to agent B. Agent B calls a database through an MCP tool and passes the result to agent C, which drafts a message to a customer. Each step crosses a trust boundary with its own authentication, permissions and log. Each agent sees its own step, and nobody sees the chain unless the enterprise builds the view.
Three rules keep the chain governable:
- Authority narrows down the chain. When one agent delegates to another, the second agent's authority is bounded by the first, and the first by the person who delegated to it. Authority never widens along the chain. The AI agent authorization guide covers how authority is computed on each request.
- Every call is authenticated. The six agencies tell developers to "Authenticate all inter-agent and agent-to-service API calls using mutual transport layer security to ensure non-repudiation."
- One identifier joins the record. An identifier carried through every task, tool call and model call rebuilds the chain from one record. The same guidance asks: "Integrate unified audit logs for all inter-agent interactions to maintain observability of all agent exchanges."
Our February post on the agent-to-agent future set out the chain problem.
An AI agent governance framework: six controls
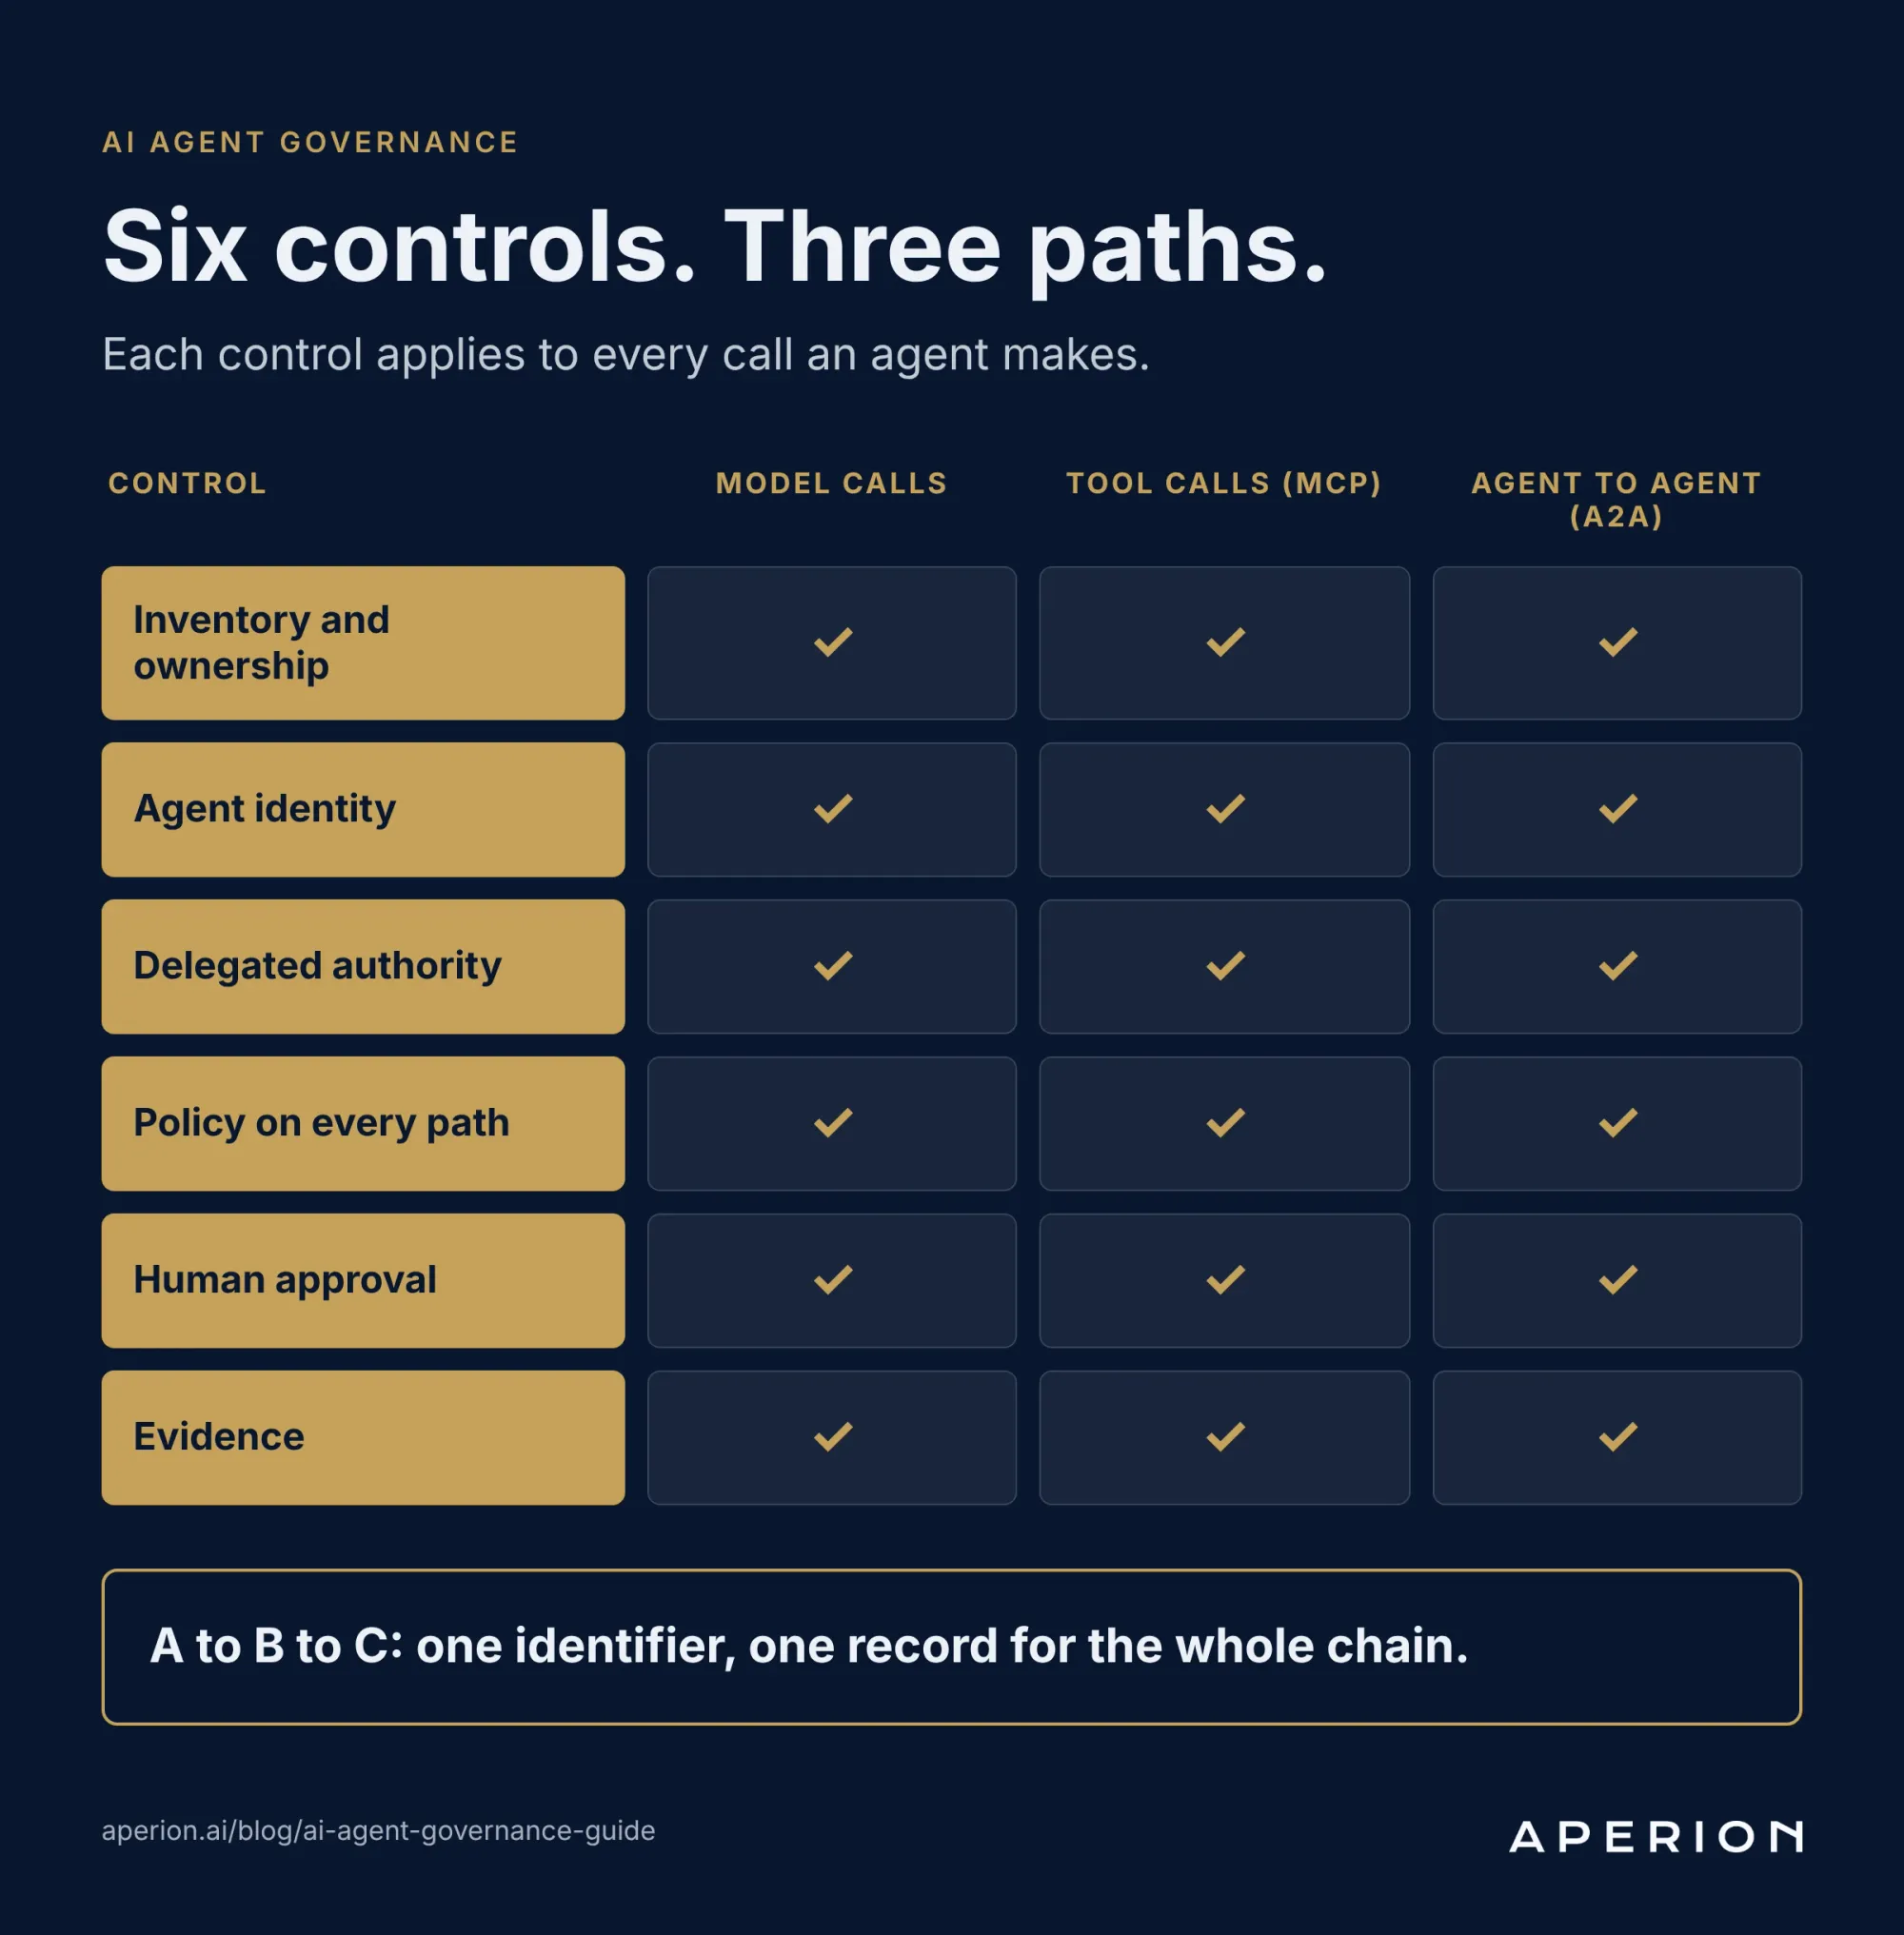
A governed agent estate has six controls, and each has to work the same way on the model path, the tool path and the agent-to-agent path, whichever provider runs the model.
| Control | The question it answers | What good looks like | Reference |
|---|---|---|---|
| Inventory and ownership | Which agents run, and who owns each one? | Every agent, tool, MCP server and A2A endpoint listed with an accountable person | NIST AI RMF, GOVERN 1.6 |
| Agent identity | Which agent is this, and whose authority is it using? | Each agent a distinct principal with credentials of its own, bound to the person who delegated to it | Five Eyes guidance, April 2026 |
| Delegated authority | What may this agent do right now? | Authority read on each request from the person's current entitlements, the scope delegated and the agent's registration | NIST SP 800-207, per-session access |
| Policy on every path | Is this call, with these arguments, inside policy? | One policy, decided before the call executes, on prompts, responses, tool calls and agent-to-agent calls | MCP specification, security principles |
| Human approval | Who decides a high-risk action? | A named person approves payments, record changes, external messages and deletions before they run | Five Eyes guidance, April 2026 |
| Evidence | Can the enterprise prove what happened? | One record per action, joined across the chain, kept with the enterprise's other regulated records | EU AI Act, Article 26(6) |
1. Inventory and ownership
The NIST AI Risk Management Framework makes the inventory a governance outcome. GOVERN 1.6 reads: "Mechanisms are in place to inventory AI systems and are resourced according to organizational risk priorities." NIST's MANAGE 2.4 adds the other end of the life cycle: mechanisms "to supersede, disengage, or deactivate AI systems that demonstrate performance or outcomes inconsistent with intended use." The shadow AI guide covers finding what the inventory misses.
2. Agent identity
The six agencies tell developers to "construct each agent as a distinct principal, a cryptographically anchored identity," with "its own unique keys or certificates." An agent that borrows a person's key cannot be revoked without disabling the person, and its actions cannot be told apart from theirs. The agent identity guide and the agent authority scope entry cover identities and their limits.
3. Delegated authority
A credential records what was true on the day it was issued. The person behind the agent changes roles, limits and employers. NIST SP 800-207 set the expectation for people and devices: "Access to individual enterprise resources is granted on a per-session basis." An agent can make many calls in one session, so for an agent, authority is checked on each request.
4. Policy on every path
Policy is decided before the call executes, written once and applied to every prompt, response and tool call, whether the model is rented or owned. Agent-to-agent calls go through the same policy. The AI control plane guide and the enterprise AI gateway guide cover where that enforcement point sits, and the glossary defines runtime governance.
5. Human approval on high-risk actions
The six agencies tell operators to "Prevent agents from autonomously executing high impact actions or outputs without prior human approval." A payment, a change to a customer record or a message sent in the firm's name pauses until a person with approval rights decides, and the decision joins the record. The step-up approval guide covers how a step-up works and which actions should require one. The glossary entry on human in the loop separates gating an action from monitoring it afterward.
6. Evidence
Each record names the person, the agent, the model and its version, the provider, the policy that applied and who approved any exception. It reads the same whichever model did the work, and it sits with the enterprise's other regulated records. The tamper-evident audit log entry covers what makes a record evidence.
What regulation and guidance ask of agents
The EU AI Act places its deployer duties in Article 26. Deployers of high-risk AI systems "shall assign human oversight to natural persons who have the necessary competence, training and authority, as well as the necessary support" (Article 26(2)), monitor the system's operation (Article 26(5)), and keep the logs it generates, to the extent they are under the deployer's control, "for a period appropriate to the intended purpose of the high-risk AI system, of at least six months" (Article 26(6)). Regulation (EU) 2026/1744, the AI Omnibus, in force since July 27, 2026, set the dates: the rules for stand-alone high-risk systems under Annex III apply from December 2, 2027, and for high-risk systems embedded in products under Annex I from August 2, 2028. An agent falls under these duties when its use falls in a high-risk category.
The Five Eyes guidance carries no legal force. Its controls match the framework above: distinct agent identities, authenticated inter-agent calls, human approval before high-impact actions and unified audit logs.
Questions to ask about your own agents
- How many agents run today, which tools and other agents can each one reach, and who owns each?
- When a person changes roles or leaves, when does the agent's authority change?
- Does one policy cover model calls, tool calls and agent-to-agent calls?
- Which actions pause for a named person, and who is that person?
- If an examiner asks what a chain of three agents did for one customer, can you answer from one record?
How APERION approaches AI agent governance
Owned intelligence, governed from the first call. APERION future-proofs the hybrid AI estate: every agent and every model an enterprise rents or owns, governed from one control point inside its own walls. Enterprises will rent some intelligence and own more of it.
The control point sits in the path between agents and every model and tool they call, rented or owned, and keeps each action inside the authority a person delegated. Global policy. Local enforcement. Portable evidence.
The Trust Fabric sets out the four layers underneath: verified identity, access governance, runtime governance, and audit and evidence.
The proof is one call. An agent tried to wire $50,000 nobody approved. The amount exceeded the authority delegated to the agent. The action paused and went back to the person whose authority the agent was using, who decided with proof they were there. The accountable human decides, and the record shows who decided, when and under which policy.
A verified person, the authority that person delegated, the agent that used it, the policy that applied, the decision and the record of all of it. That chain is the product.
Frequently asked questions
What is AI agent governance?
AI agent governance is the set of controls that keeps every action an AI agent takes inside the authority a person delegated, across calls to models, to tools over MCP and to other agents over A2A. For each action it establishes which agent acted, whose authority it used, which policy applied and who decided anything high-risk, before the action runs, and keeps that in a record.
What is an AI agent governance framework?
A framework is the set of controls an enterprise applies to every agent. A workable one has six: an inventory with an owner on every line, a distinct identity for each agent, authority read from the person's current entitlements on each request, one policy on every path, a named person approving high-risk actions, and one record per action that joins every step of a multi-agent chain.
How is agentic AI governance different from model governance?
Model governance asks whether a model is fit for a use: its data, its testing and its performance. Agentic AI governance asks whether a specific action is inside a person's delegated authority at the moment the agent takes it. An agent can use a well-tested model and still send a payment nobody approved, so agents need controls on actions as well as on models.
What is the A2A protocol, and why does it matter for governance?
Agent2Agent (A2A) is an open protocol for agents to find each other through Agent Cards and hand off work as tasks. Google announced it in April 2025, and it is now a hosted project of the Agentic AI Foundation, under the Linux Foundation. It matters because a task can pass through several agents, each with its own tools and log, so the enterprise needs one record of the chain.
Does MCP handle security for AI agents?
Partly. The MCP specification sets security principles, including explicit user consent before any tool runs, and it provides authorization capabilities at the transport level, which it makes optional. It also states that MCP itself cannot enforce those principles at the protocol level. Deciding whether a specific tool call is inside a person's authority, and recording it, falls to the enterprise running the agents.
Does the EU AI Act apply to AI agents?
It applies when an agent's use falls in a high-risk category. Article 26 then requires deployers to assign human oversight to competent people, monitor operation and keep the system's logs for at least six months. Under Regulation (EU) 2026/1744, those duties apply to stand-alone high-risk systems from December 2, 2027, and to high-risk systems in regulated products from August 2, 2028.
Sources
- Model Context Protocol, Specification and Authorization, version 2026-07-28. Opened November 20, 2026.
- Google Developers Blog, Announcing the Agent2Agent Protocol (A2A), April 9, 2025. Opened November 4, 2026.
- The Linux Foundation, Linux Foundation Launches the Agent2Agent Protocol Project to Enable Secure, Intelligent Communication Between AI Agents, June 23, 2025. Opened November 4, 2026.
- Agentic AI Foundation, A2A joins AAIF's open agentic stack, August 17, 2026. Opened November 4, 2026.
- A2A Protocol, Specification, latest released version 1.0.0. Opened November 20, 2026.
- OWASP GenAI Security Project, OWASP Top 10 for Agentic Applications for 2026, December 9, 2025, and the release announcement. Opened November 4, 2026.
- ASD's ACSC, CISA, NSA, Canadian Centre for Cyber Security, NCSC-NZ and NCSC-UK, Careful Adoption of Agentic AI Services, and the NSA's release announcement, April 30, 2026. Opened November 4, 2026.
- Fortune, An AI-powered coding tool wiped out a software company's database, then apologized for a 'catastrophic failure on my part', July 23, 2025. Opened November 4, 2026.
- NIST, Artificial Intelligence Risk Management Framework (AI RMF 1.0), NIST AI 100-1, January 2023. Opened November 4, 2026.
- NIST, SP 800-207, Zero Trust Architecture, August 2020, Section 2.1, tenet 3. Opened November 4, 2026.
- EU Artificial Intelligence Act, Article 26, Obligations of deployers of high-risk AI systems. Opened November 4, 2026.
- Official Journal of the European Union, Regulation (EU) 2026/1744, July 8, 2026, and the European Commission, AI Omnibus enters into force, July 27, 2026. Opened November 4, 2026; Commission page reopened November 20, 2026.
Related reading
Put this in the path of your own agents.
Policy enforced inline between your agents and every model and tool they reach, with a record bound to the human who owns it.
Request a Demo Read the docs