Regulatory summaries verified as of October 26, 2026.
The problem in one paragraph
A hotel group running properties in mainland China, Saudi Arabia and Europe operates under three regimes that disagree about where guest data may sit and who may see it. The AI layer makes that disagreement operational. A guest-messaging assistant that summarizes a stay, a revenue model that reads booking history, a loyalty assistant that answers a member's question: each one moves personal data into an inference call. If that call leaves the jurisdiction, a routine product feature becomes a cross-border transfer, and the group has created a compliance question nobody signed off on.
One guest, one week, three rulebooks
Follow one loyalty member through one week. She enrolled in Germany. She stays in Frankfurt on Monday, Riyadh on Wednesday and Shanghai on Friday.
At each property the same three things happen. The messaging assistant reads her preferences and drafts a welcome note. The front desk asks an agent to move her late checkout and credit points for a noisy room. The loyalty assistant answers a question about her tier. Every one of those calls carries her personal data, and the rules accumulate: the European rules that came with her record, plus the rules of each city where the call is processed.
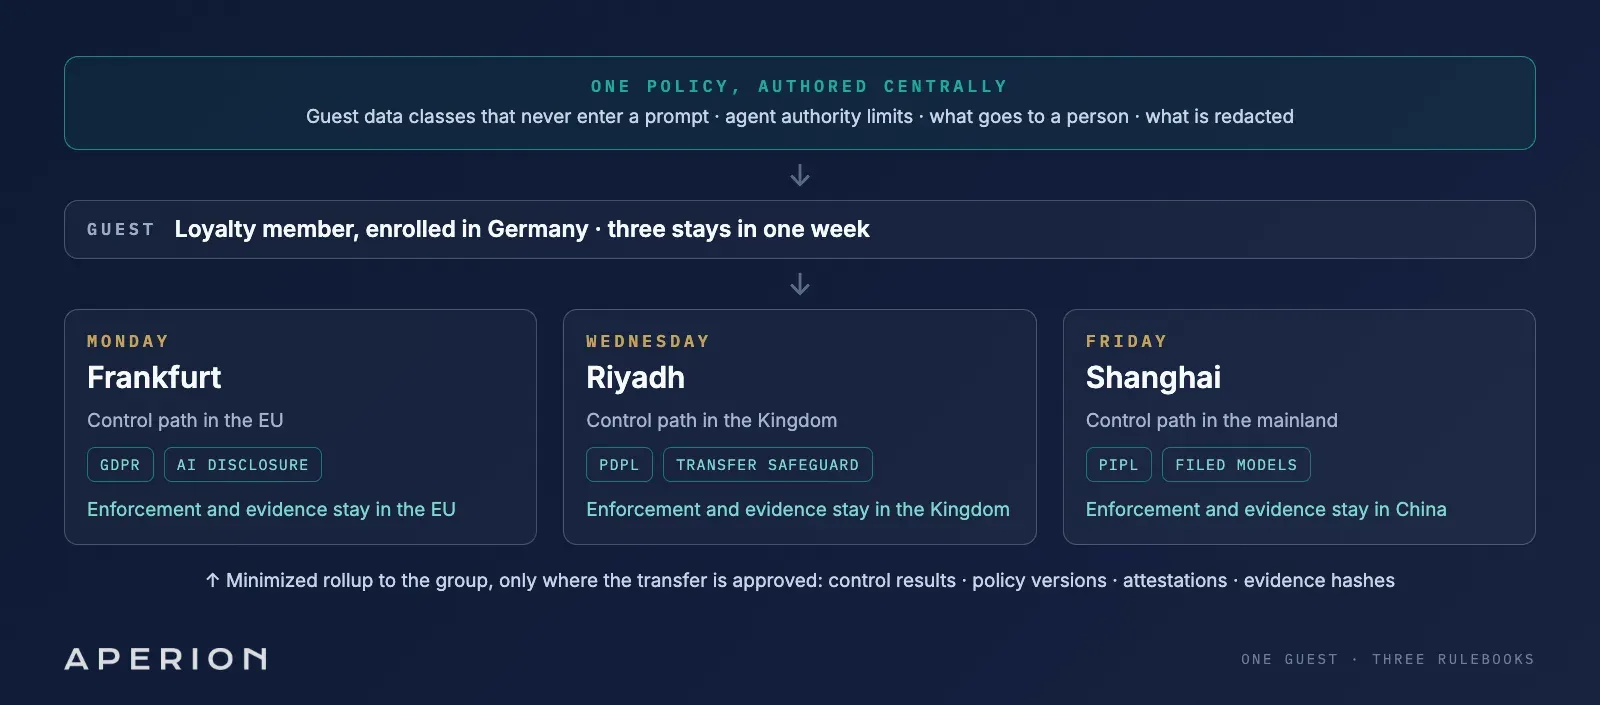
- Frankfurt. GDPR governs her data. The messaging assistant has to tell her she is talking to an AI system. Her record can move within the EU, and the group's EU instance keeps the evidence.
- Riyadh. Sending her EU record to Riyadh, or to Shanghai, is a GDPR transfer, so the European rules travel with it. Saudi Arabia's Personal Data Protection Law adds its own rules for processing in the Kingdom. If the property's AI call sends her data to a model outside the Kingdom, that is a transfer that needs a recognized safeguard and, in most cases, a written risk assessment first.
- Shanghai. China's Personal Information Protection Law governs her data once the property processes it. Sending her reservation details abroad to perform the booking falls under a specific exemption. Sending the same details to an overseas model for a summary is a different purpose and needs its own basis. A guest-facing assistant offered in mainland China also has to run on a model that has completed CAC filing.
One guest, one week, three different answers to the same question: where may this inference call run? A group that cannot answer it per property, per call, has an AI program it cannot defend.
Why hospitality is a harder case than most
Guests cross borders by definition. A record collected in one country is processed in several. Each market where it is processed adds its own rules to the ones the record carries from where it was collected.
The estate is mixed. Owned, managed and franchised properties sit under different contractual and technical control. Central IT does not have uniform administrative reach into every property system.
Property-level IT is thin. The control has to be deployable and operable centrally, not configured by a front-desk system administrator in each market.
Volume is seasonal and spiky. Peak periods produce inference volumes that make per-call human review impossible and make cost exposure visible.
Payment cards are everywhere. Card data that reaches a prompt brings that model path into PCI DSS scope. Redacting card numbers before the prompt reaches a model keeps card data off the model path. The redaction step itself handles card data, so it sits inside PCI scope.
The guest is the user. Many hotel AI systems face the public directly. In mainland China that brings service registration an employee-only tool would not trigger. In the EU, the duty to disclose AI interaction covers guests and staff alike.
The three regimes, in operational terms
Verified as of October 26, 2026.
Mainland China
The Personal Information Protection Law, the Data Security Law and the Cybersecurity Law, which was amended with effect from January 1, 2026, set the frame. Personal information sent out of the mainland needs a legal mechanism: a CAC security assessment, the standard contract or certification, depending on volume and sensitivity.
The Provisions on Promoting and Regulating Cross-Border Data Flows, in force since March 22, 2024, exempt some transfers from those mechanisms. One listed example is personal information that is truly necessary to provide abroad to conclude or perform a contract, and plane and hotel reservations are named. That exemption covers the reservation. It is hard to stretch it to an inference call that sends a guest's details to an overseas model for a summary, which serves a different purpose. The exemption removes the CAC mechanism only. PIPL's notice, consent and impact-assessment duties still apply.
Generative AI services offered to the public fall under the CAC's interim measures. A service built on a model through an API is registered with the local cyberspace authority, and it can only take that route if the underlying model has completed CAC filing. Use limited to the company's own employees generally falls outside that regime. AI-generated content shown to the public also carries labeling duties.
Practical consequence: guest personal information used in an inference call should be processed by a model deployed inside the mainland, guest-facing assistants should run on filed models, and the resulting records should stay in China. The full China architecture is in One global AI policy plane, including China.
Saudi Arabia
The Personal Data Protection Law has been fully enforceable since September 14, 2024. Its transfer regulation, updated in September 2024, allows personal data to leave the Kingdom on an adequacy decision or an appropriate safeguard: the standard contractual clauses, binding common rules for a corporate group, or a certificate of accreditation. As of September 2026, SDAIA had published no adequacy list, so a hotel group's transfers out of the Kingdom rest on a safeguard. A risk assessment is required before a transfer under a safeguard, and for continuous or large-scale transfers of sensitive data.
SDAIA's AI Ethics Principles set national expectations across seven principles: fairness; privacy and security; humanity; social and environmental benefits; reliability and safety; transparency and explainability; and accountability and responsibility.
Practical consequence: a deployment resident in the Kingdom, with local log retention, a documented account of what each AI system does and who is accountable for it, and a transfer file for anything that leaves.
European Union
GDPR governs the personal data. The EU AI Act adds duties by use. Since August 2, 2026, a system that interacts with people has to tell them they are dealing with AI, which reaches every guest-facing assistant. The high-risk obligations for uses listed in Annex III, which include AI used in hiring and managing staff, apply from December 2, 2027 under the amendment adopted in July 2026.
Practical consequence: disclosure built into every guest-facing flow now, and evidence that can be produced for a specific system and a specific period, ready before the high-risk duties reach the group's HR systems.
A policy document satisfies none of these. Each depends on where enforcement runs and what evidence exists afterward.
The architecture that resolves it
The pattern is global policy, local enforcement, portable evidence.
One policy, authored centrally. The global security team writes the rules once: which categories of guest data may never enter a prompt, which agents may change a booking or credit points, what requires a human decision, what gets redacted.
Enforcement inside each jurisdiction. Smartflow is designed to run the control path inside the customer-controlled environment in mainland China, Saudi Arabia, the European Union, the United States and other regulated markets. Common policy definitions can travel. Enforcement, provider credentials, governed traffic and required evidence stay inside the regional boundary. Each regional instance routes to endpoints permitted in that market, including models the group hosts itself and regional cloud model services.
Evidence created where the interaction happened. The audit record is written in the jurisdiction of the interaction and stays there. Where the deployment supports it and the transfer is approved, the group receives a minimized operational rollup: control results, policy versions, attestations and evidence hashes. Raw prompts, responses and personal data are not copied out.
The line to draw in an architecture review: common policy definitions can travel, governed content cannot.
Six workloads, governed
Guest messaging and concierge. Passport numbers, payment identifiers and health or accessibility notes are classified and redacted before the prompt reaches a model. The redaction is logged, so a regulator asking what the model saw gets an answer rather than an assurance. Guest-facing flows carry the AI disclosure the EU requires, and in mainland China they run on filed models.
Reservations and service recovery. Agents that move a reservation, issue a refund or credit points are where money moves. Agent credentials bind each agent to a named human principal, with defined action scopes and transaction limits, so every action is attributable to a person rather than a service account.
Revenue management and forecasting. These models read booking and rate history at volume. Routing keeps each workload on the endpoint permitted in its market, and task routing sends the high-volume, low-complexity share to a cheaper model without an application change.
Loyalty and member service. The loyalty record is the one that travels. Each property's assistant reads what it needs under the rules of the market where it runs, and the evidence of what it read stays there.
Group sales and events. Assistants that draft responses to corporate group requests read client contracts and rate agreements. Policy keeps that material inside the market where it sits and records which assistant saw which document.
Staff copilots and HR. Staff use of AI is where uncontrolled data movement usually starts. A sanctioned path with policy in front of it is the control that scales across a large, distributed, high-turnover workforce. AI used in hiring and staff management is the first hotel workload the EU's high-risk duties reach.
The authority question at the front desk
A front-desk manager can comp a night or credit points up to a limit the group sets. When an agent acts for that manager, it acts on her authority, inside her limit. A credit inside the limit goes through and is recorded against her name. A credit above it goes back to her, and she decides. The record shows the agent, the person, the authority used and what the agent saw.
That chain is the product: a named person, the authority she delegated, the action taken, and evidence a regulator can examine.
Franchised and managed properties
The control sits in the AI request path. A franchised property that calls the governed endpoint is covered without central administrative access to its local systems. The group sets the policy floor, and the franchise agreement can require that property AI traffic use the governed endpoint. A property that bypasses it shows up as a property with no records.
Why cloud AI gateways are structurally hard here
The constraint is topology. A managed gateway that terminates API traffic in its own cloud, or aggregates telemetry centrally, creates a transfer event on every call and a second copy of the record outside the jurisdiction. That is a defensible design for a single-market company and a difficult one to explain to a regulator in a market with residency requirements.
Smartflow is deployed as software inside the customer environment. No request, prompt, response or cached artifact traverses APERION infrastructure. There is no tier that changes this.
The evaluation questions for an RFP
- Where does the control path run in each market, and who operates it?
- What leaves the jurisdiction, precisely, including telemetry and metrics?
- Can one policy definition be authored centrally and enforced locally without a per-market rewrite?
- Can the audit record produce evidence for a named system over a named period?
- What happens to enforcement and logging when a regional model endpoint fails?
- Which endpoints can be registered in each market, including models the group hosts itself?
- Is every agent action attributable to a named human principal, with the authority that person delegated?
- What does the deployment require from property-level IT, realistically?
- Which guest-facing assistants tell the guest they are talking to AI, and where is that recorded?
- Which models behind public-facing services in mainland China have completed CAC filing?
Frequently asked questions
Can AI agents be used at properties in mainland China without transferring guest data abroad? Yes, if inference runs against a model deployed inside the mainland and the layer that enforces policy and writes audit records also runs inside the mainland. The usual failure is a gateway or observability service that ships telemetry out by default.
Does China's exemption for hotel reservations cover AI? It covers personal information that is truly necessary to provide abroad to make or perform the reservation. An inference call that sends guest details to an overseas model serves a different purpose, and it is hard to fit inside the exemption. Confirm the analysis with counsel for each workload.
Does one global AI policy work across China, Saudi Arabia and the EU? One policy definition can be authored globally. Enforcement and evidence must be local. The workable model is a shared policy language with jurisdiction-specific parameters, enforced in each market.
What does Saudi Arabia require before guest data leaves the Kingdom? A permitted purpose, the minimum data necessary, and an adequacy decision or an appropriate safeguard. With no adequacy list published as of September 2026, that means the standard contractual clauses, binding common rules or a certificate of accreditation, with a risk assessment in most cases.
Do guest-facing chatbots in the EU have to disclose that they are AI? Yes. Since August 2, 2026, the AI Act requires systems that interact with people to tell them so, unless it is obvious from the context.
How does this handle franchised properties? The control sits in the AI request path, so a franchised property that calls the governed endpoint is covered without central administrative access to its local systems.
What is the difference between this and an AI firewall? An AI firewall inspects content. This includes that, and adds identity-bound enforcement, routing and failover across permitted endpoints in each market, and evidence a regulator can examine.
Regulatory summaries are general and current as of October 26, 2026. They are not legal advice. Confirm requirements with counsel in each jurisdiction.
Put this in the path of your own agents.
Policy enforced inline between your agents and every model and tool they reach, with a record bound to the human who owns it.
Request a Demo Read the docs